
Key Takeaways
- Disconnecting infected machines without powering them off is usually the right first move, since shutting down can erase evidence stored in memory.
- A tested recovery plan with critical systems listed in order can make the difference between a few days of disruption and several weeks of lost business.
- Paying a ransom does not guarantee files come back and does not remove the need to find how attackers got in, rebuild systems, and restore backups.
- Finding the entry point before restoring anything prevents businesses from reinfecting freshly rebuilt systems.
- Treating backups as offline and verified before trusting them for restoration is a step many businesses skip until it’s too late.
A ransomware attack rarely announces itself politely. One minute the office network is running fine, and the next, files are locked and a note demands payment. What happens in the hour after that discovery often decides whether a business is back to work in a few days or still cleaning up a month later.
Unplug First, Then Call Your IT Provider
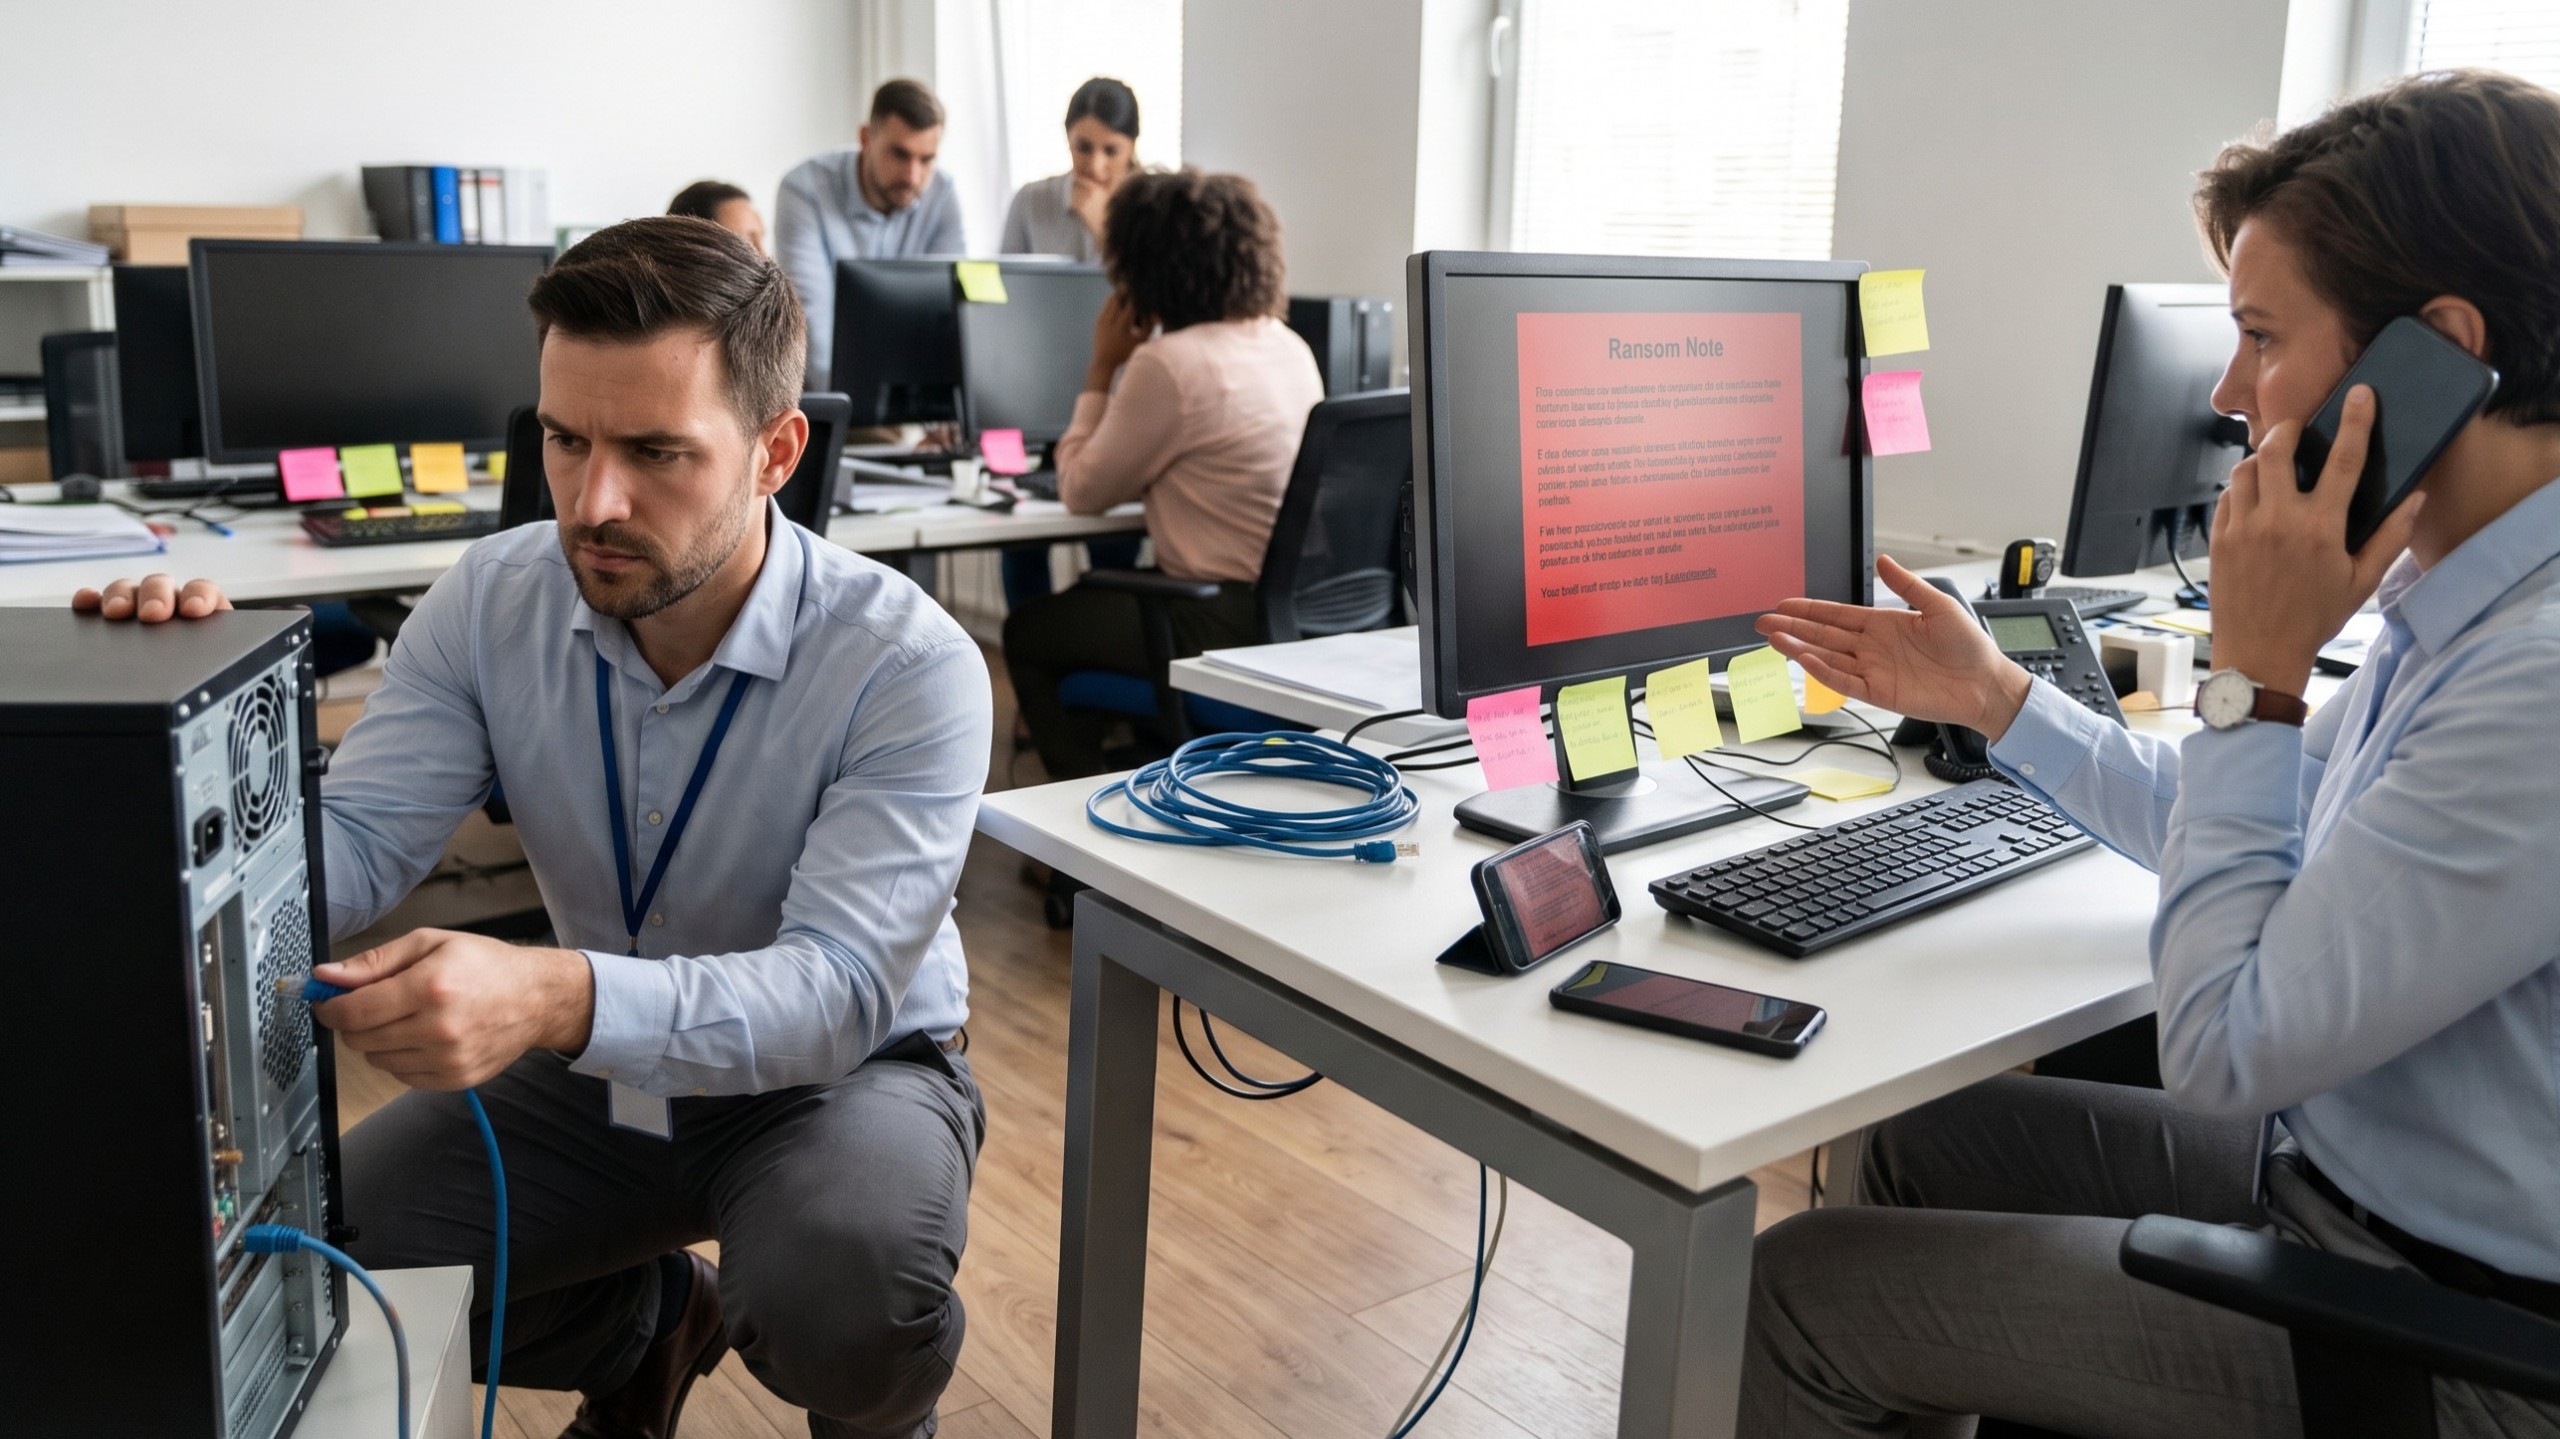
The instinct to start fixing things immediately is understandable, but the first move should be the simplest one: disconnect the infected machine. Pull the network cable or turn off the Wi-Fi connection, then bring in the IT team. Trying to diagnose the problem before cutting off the connection gives the ransomware more time to spread to other devices on the same network.
This order matters more than it might seem. Restoring systems too quickly can reinfect everything, while wiping devices too fast can destroy evidence that an insurance carrier or law enforcement agency may need later. Texas-based Function-4 walks businesses through this sequence, closely mirroring guidance from the federal Cybersecurity and Infrastructure Security Agency (CISA): contain first, investigate second, rebuild and restore only after the entry point is confirmed closed.
Contain the Attack Within the First Hour
Ransomware spreads fast across a network, scanning for other vulnerable devices and encrypting whatever it can reach. Every extra minute a machine stays connected raises the number of files at risk, so containment has to happen before anything else, including troubleshooting.
Disconnect Devices Without Powering Them Off
Pulling the network cable or disabling Wi-Fi isolates an infected device while keeping it running. If several systems appear to be affected at once, taking the network offline at the switch level may be the faster way to stop the spread across an entire office or building. Powering a device down should be a last resort, reserved for situations where disconnecting it from the network isn’t possible any other way, since shutting it off can wipe out memory that holds clues about how the attack unfolded.
Switch to Phone Calls, Not Email
If attackers are still inside the network, they may be reading email as it arrives. Coordinating a response over a compromised inbox can tip them off that the business has noticed the breach. Phone calls or another communication channel outside the network keep the response team’s next steps private while containment work gets underway.
Preserve the Ransom Note and Document Everything
The ransom note itself is evidence, so it should be left alone. Photographing it with a separate device works well, and clicking any links inside it or replying to the attackers is not advisable at this stage. Alongside the note, keeping a simple log of what was noticed and when, plus who got called and at what time, builds a timeline that insurers and investigators will both ask for later.
Who to Contact After an Attack
The list of calls to make is longer than most business owners expect. An IT or managed security provider typically leads the hunt for how attackers got in and manages the technical rebuild that follows. A cyber insurance carrier should be contacted early too, since many policies specify which response firms a business is allowed to use, and finding that out after hiring someone can create complications.
Federal law enforcement plays a role as well. Incidents can be reported to CISA, a local FBI field office, or the FBI’s Internet Crime Complaint Center, and it’s worth asking whether a free decryptor exists for the specific ransomware strain involved. When customer or employee data may have been accessed, bringing in an attorney matters too, since breach notification laws often carry their own deadlines that start ticking the moment the incident is confirmed.
Should You Pay the Ransom?
Federal guidance leans firmly against paying, for two straightforward reasons: there’s no guarantee the data comes back, and payment funds the criminal activity that keeps targeting other businesses. Even so, a large share of companies pay anyway when faced with the pressure of a shutdown.
What often gets missed is that paying doesn’t skip any of the cleanup work. The entry point still has to be found and closed, systems still need rebuilding from clean images, and every recovered file still needs testing before it’s trusted. Many ransomware attacks also involve copying data before encrypting it, a tactic known as double extortion, and a ransom payment does nothing to undo that theft. Any decision to pay should involve an attorney and the cyber insurance carrier before anyone opens a dialogue with the attackers.
Find the Entry Point Before Restoring Anything
Skipping the investigation step is one of the costliest mistakes a business can make during recovery. Restoring systems before identifying how attackers got in risks rebuilding right on top of a hidden piece of malware, sometimes called a dropper, left behind for a second attack.
Finding that entry point means digging through system logs for new or altered user accounts, unusual VPN logins, and remote-access tools nobody remembers installing. Attackers frequently target backups and shadow copies too, since destroying a business’s recovery options makes them more likely to pay, so those areas need checking as well. Only after this detective work is complete does it make sense to move forward with rebuilding.
Rebuild Clean Systems in Priority Order
Bringing every system back online at once isn’t realistic, and attempting it usually slows recovery down rather than speeding it up. A predefined list of critical systems, along with what each one depends on, lets the business-essential pieces come back first. Payroll and client-facing systems typically take priority over less urgent tools.
Rebuilt machines should start from clean, standard images rather than the infected originals. Passwords for every affected account need resetting, and the specific weakness attackers exploited has to be patched before the system goes back into service. A designated IT or security lead should formally confirm when the incident is considered closed, which keeps the recovery process accountable rather than informal.
Restore Only From Offline, Verified Backups
Backups kept separate from the main network, rather than continuously connected to it, stand the best chance of surviving an attack untouched. A backup drive that stays plugged into the network can get encrypted right along with everything else, which defeats the purpose of having it in the first place. Restoring only from backups confirmed clean, and only onto systems that have already been rebuilt and verified, keeps a business from reintroducing the same infection it just removed.
How Long Does Recovery Actually Take?
Encryption can happen overnight, but getting a business fully back to normal almost always takes longer, typically measured in days or weeks rather than hours. The gap between those two timelines is exactly why containment and investigation can’t be rushed. Cutting corners early tends to add time later rather than save it.
Recovery costs extend well past any ransom figure. Downtime, lost orders, staff overtime, and the cost of outside help to rebuild systems all add up, and businesses without tested backups or a practiced response plan tend to feel every one of those costs more sharply.
Closing the Door the Attackers Used
Once systems are back up and running, the work remains unfinished. Whatever let the attackers in, whether a stolen password, an unpatched server, or a phishing email that tricked an employee, needs a permanent fix, because attackers who found a way in once often try the same path again.
A few habits make that door harder to reopen:
- Turning on multi-factor authentication everywhere it’s available, starting with email and remote access
- Testing backups regularly, since a backup that’s never been restored is a guess rather than a safety net
- Keeping at least one backup copy offline or isolated from the main network
- Training staff to recognize phishing attempts, which remain one of the most common ways ransomware gets a foothold
A Tested Recovery Plan Determines How Fast Business Resumes
A written ransomware response plan works best when it lists critical systems in the order they need to come back, notes where clean backups live, and includes phone numbers for the IT provider and insurance carrier. None of that helps if it’s stored only on a server that ends up encrypted, so a printed copy kept somewhere accessible is worth the extra step.
Practicing the plan before an attack happens matters just as much as writing it. A plan nobody has rehearsed tends to fall apart under the pressure of an actual incident, while a business that has walked through its steps in advance tends to move through containment, investigation, and restoration with far less confusion. For Texas businesses weighing where their current plan has gaps, a closer look at ransomware recovery steps developed by Function-4 is a reasonable place to start before an incident forces the issue.
Function-4
13025 Stiles Ln Suite 100
Sugar Land
Texas
77478
United States


